Autonomous end-to-end cybersecurity.
Many AIs, one answer
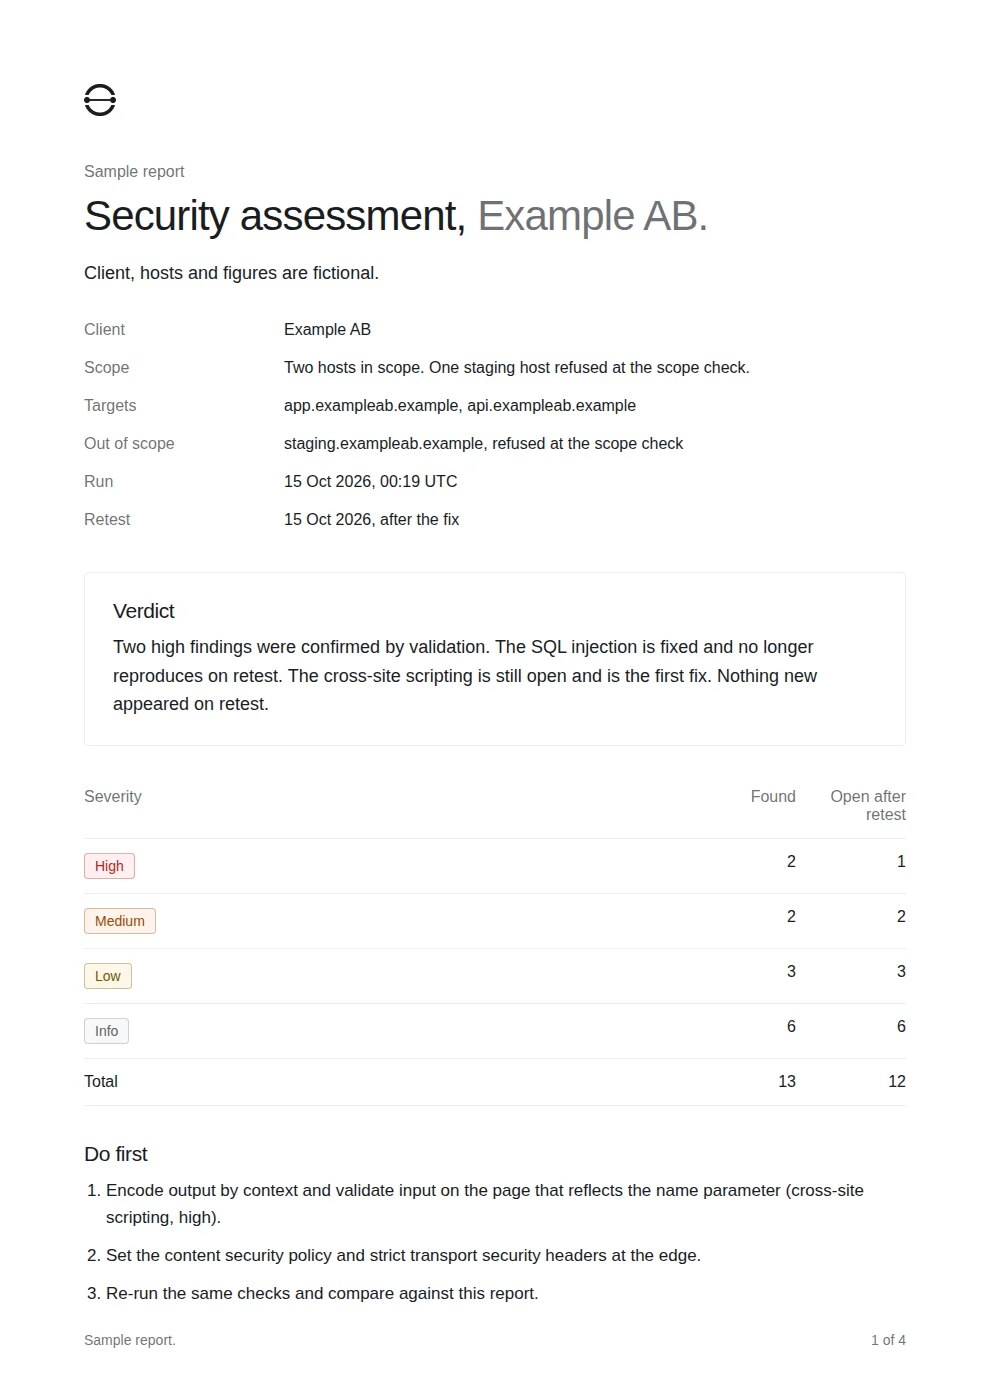
Several AI models check each other’s work. Only what is proved counts.
A record you can check
What we may test, every step we took and the proof, all signed.
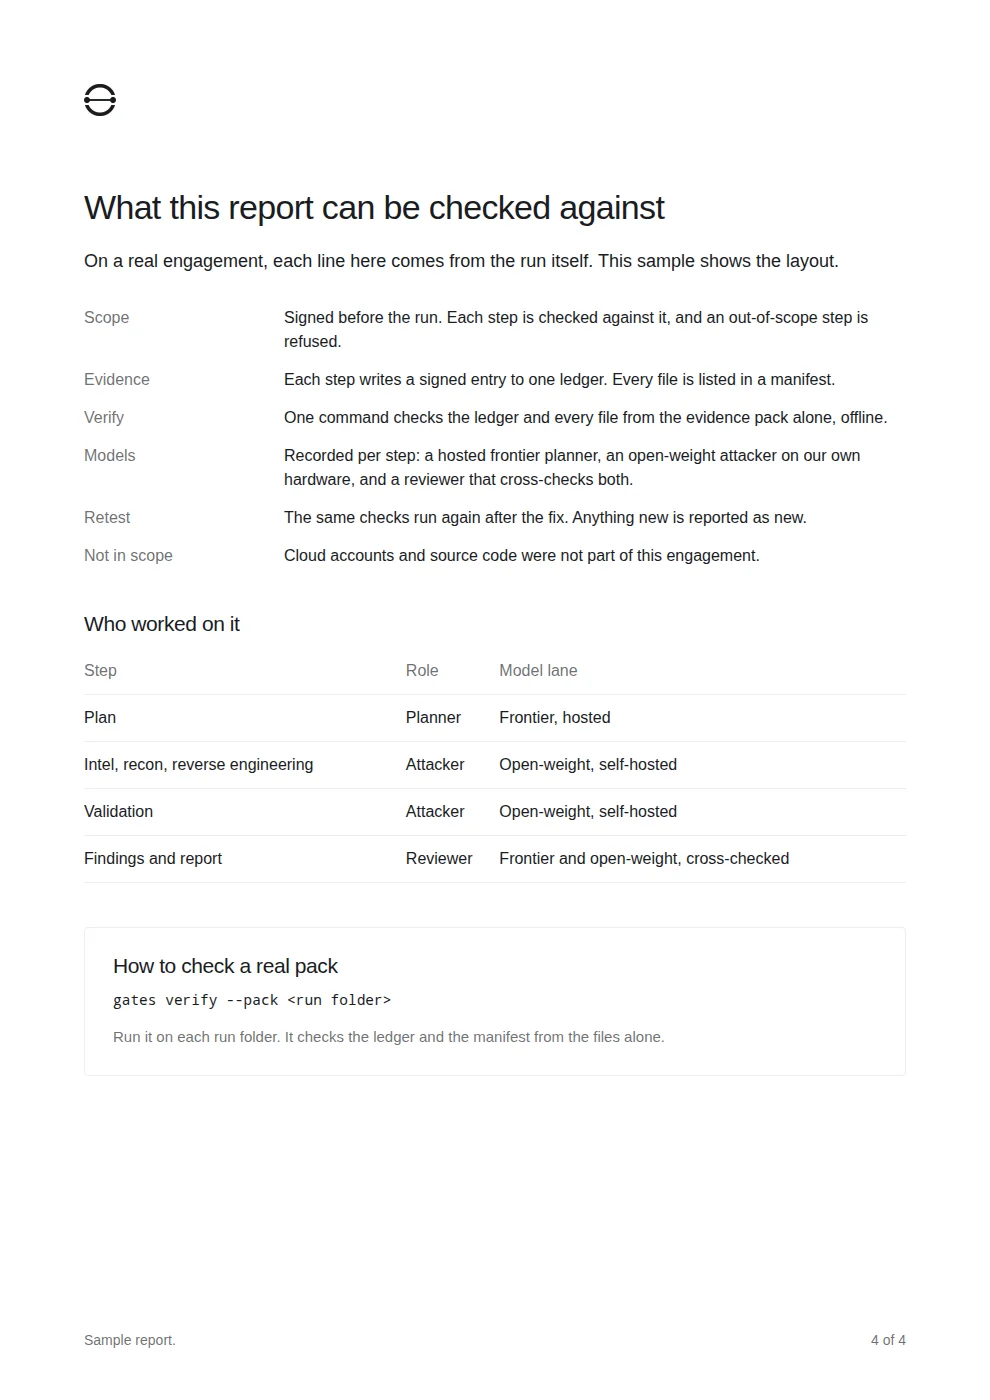
No black box
Every report names the AI models that worked on it.
Your data can stay in
The AI can run on your own machines when the data cannot leave.
Everything, end to end. From the first look to the last retest.
What you expose
What anyone can find about you online, mapped before an attacker does.
Websites and apps
Logins, accounts and the ways your app can be tricked.
Cloud
Who can reach what, and storage left open.
Code
Leaked passwords and risky code, fixed as a ready change.
Software and devices
How long your apps hold when an AI tries to take them apart.
Servers
Settings left loose and doors left open.
Alerts
Warnings for your team from every attack we prove, AI agents included.
After a breach
AI on your own machines reads what happened.
How we test. With your permission, inside the lines, stopped at proof.
-
Written authorization first
We confirm who you are and that you own each target before anything runs.
-
Scope is enforced
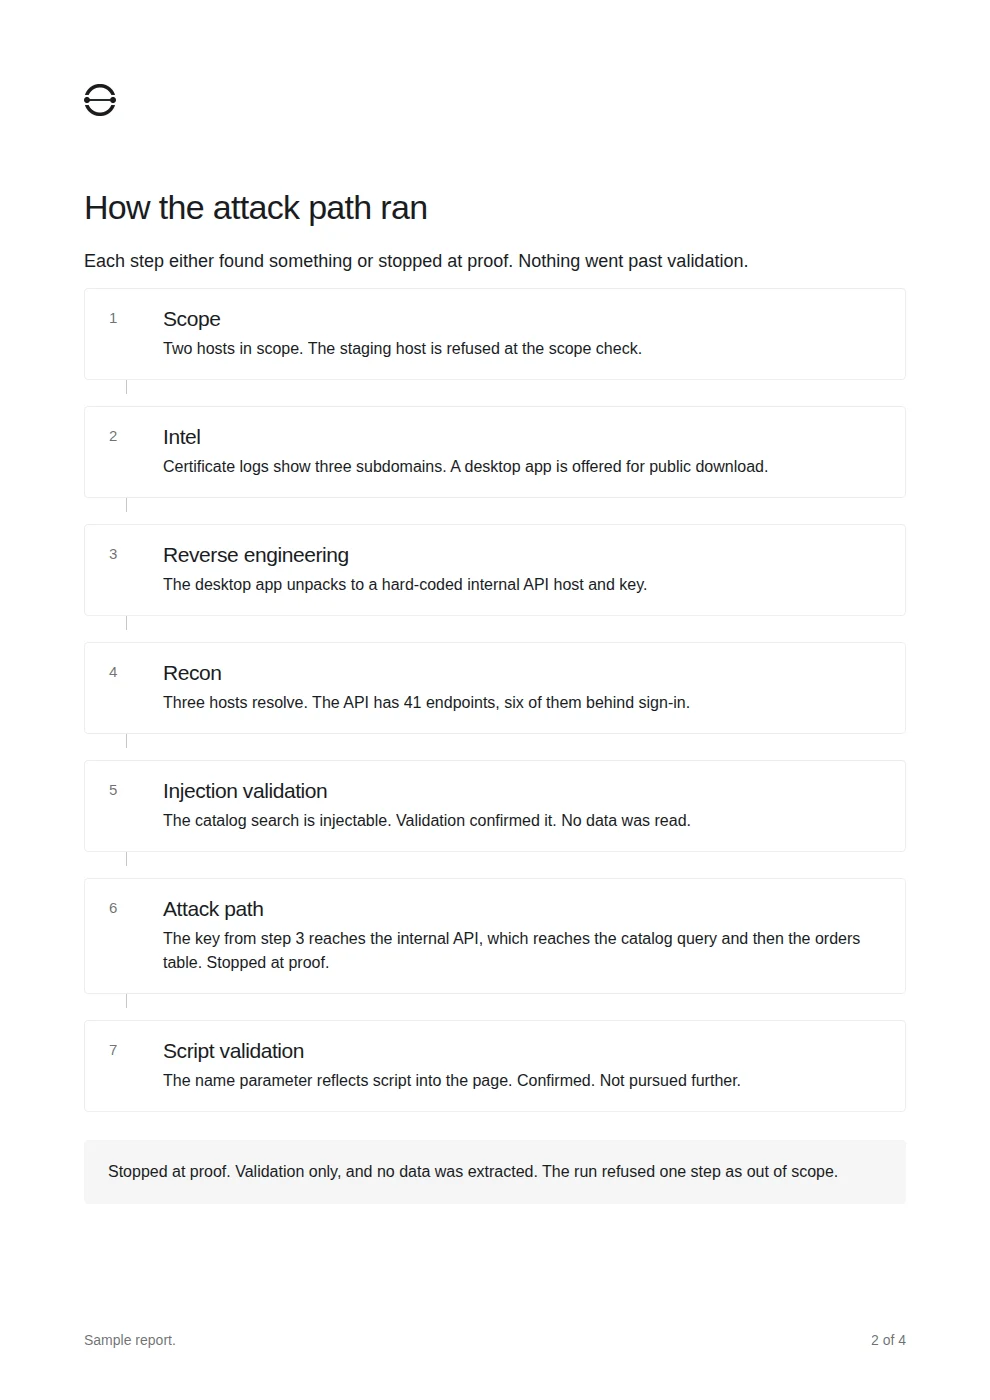
Every step is checked against the signed scope. A step outside it is refused and recorded.
-
Proof, then stop
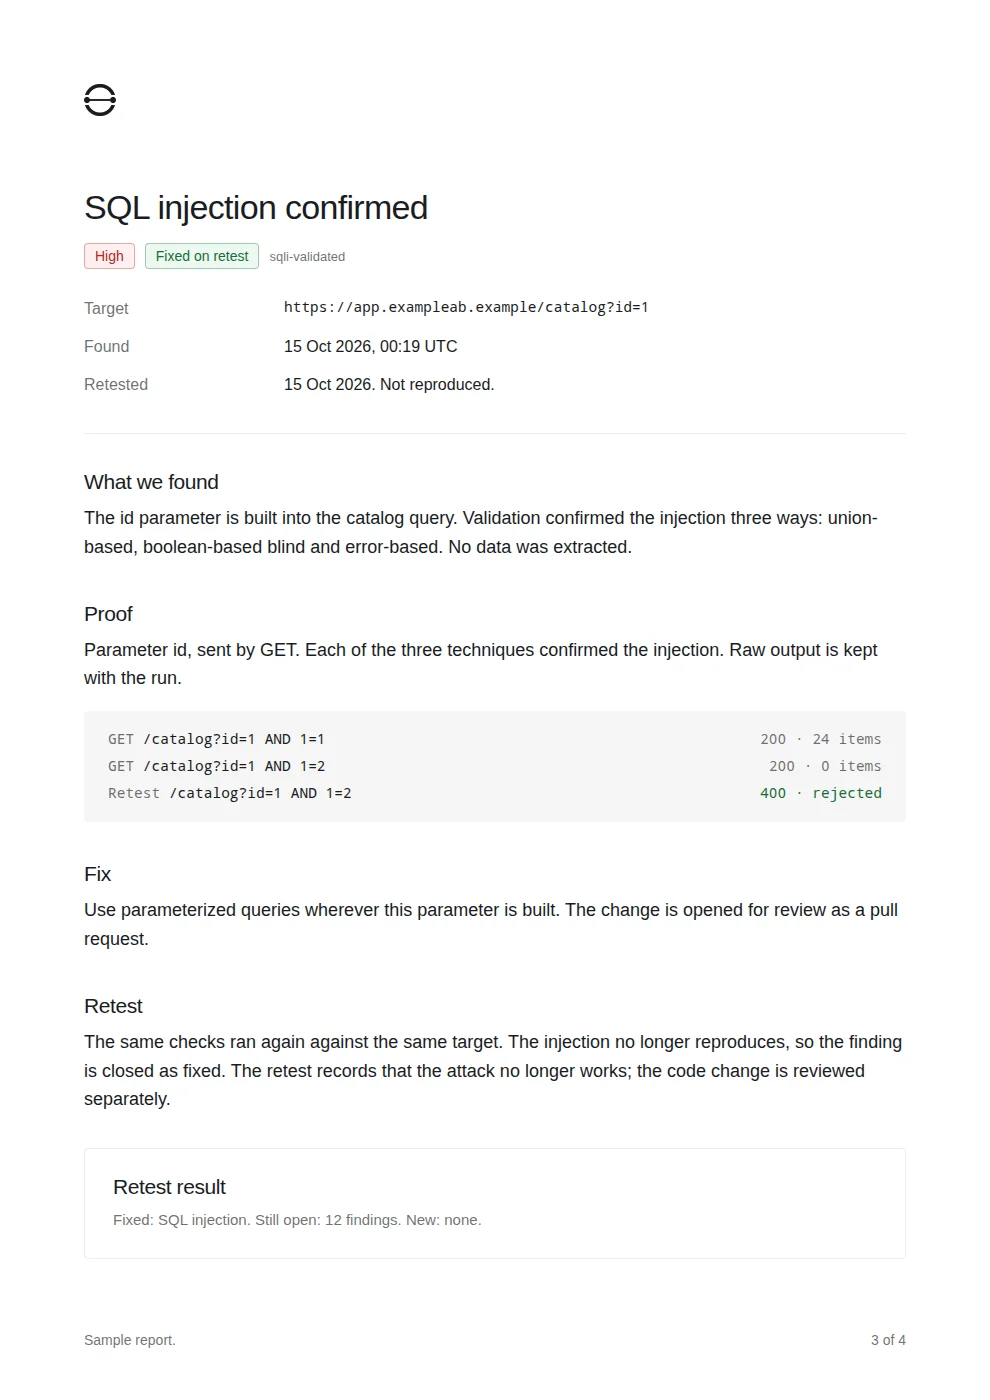
A weakness is proved once. No data taken, nothing left behind, no load on production.
-
Some work we refuse
Unauthorized targets, ransomware, surveillance of people, anything that could cause physical harm.